Product guidance
Federated Identity Management: A Practical Guide for Business Operations
Learn how federated identity management implementation and public-avatar signals help teams streamline contact-data review workflows.
Explore how federated identity management implementation centralizes access, and learn how public-avatar signals help teams review contact data across disparate platforms.
Federated Identity Management (FIM) simplifies user access by allowing a single set of credentials to work across multiple platforms, reducing password fatigue and supporting centralized security. The core mechanism involves trust agreements between identity providers and service providers, supporting single sign-on across disparate applications. For business operations, this centralized framework is complemented by tools that provide public-avatar signals and profile attributes. Platforms like AvatarLookup allow teams to effectively review and manage contact data across messaging and email services. By confirming public-avatar availability, organizations gain auxiliary profile signals that support contact-data review workflows, helping maintain accurate records alongside broader federated identity management implementation strategies.
Understanding Federated Identity Management
Modern business operations rely on seamless access to multiple applications, which is where federated identity management implementation becomes critical. This framework centralizes identity management, allowing users to authenticate once and access various interconnected systems without creating new passwords for each service. The architecture relies on established trust agreements between identity providers, who authenticate the user, and service providers, who grant access to their resources. By reducing the number of credentials users must manage, organizations decrease login friction and improve the overall user experience. Centralizing these authentication processes also supports security by minimizing the attack surface associated with multiple password-protected accounts. Administrators can manage access policies from a single control point, streamlining administrative procedures. While this framework handles authentication and authorization, organizations often need supplementary methods to review the contact data associated with these user accounts across external communication channels, helping internal directories align with reachable external identifiers.
The Role of Public Profile Signals in Identity Workflows
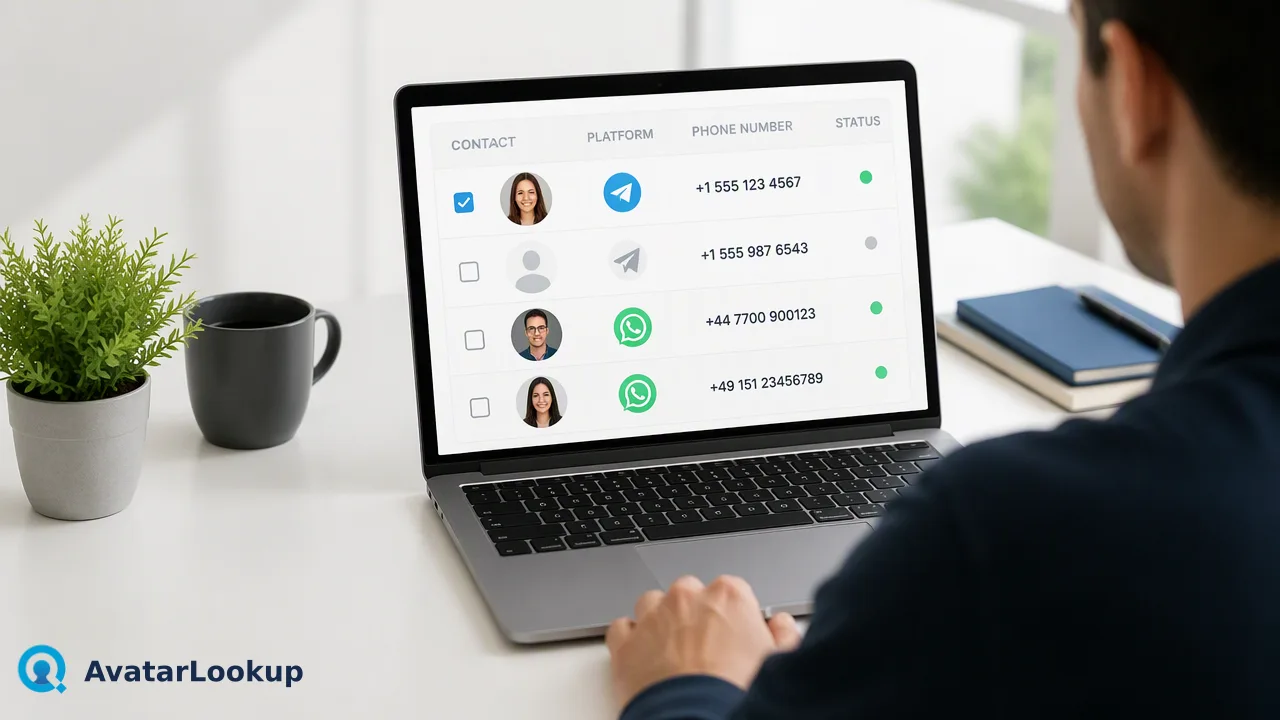
While centralized authentication manages internal access, organizations must also review external contact data. AvatarLookup operates as a focused public-avatar detection platform for teams that need to review supported account identifiers in contact-data workflows. By checking public-avatar availability, teams can gather auxiliary profile signals that inform their data hygiene processes. Single checks support platforms such as WhatsApp, Gmail, Yandex, and Mail.ru. When an organization queries a phone number or email address, the system returns a public-avatar signal indicating whether a public-facing image is associated with that identifier on the supported platform. These signals provide teams with context for their contact lists, helping them categorize and review records based on avatar presence. Integrating these checks into broader data management workflows allows organizations to maintain organized directories, complementing the internal security provided by federated identity management implementation with external contact-data visibility.
Algorithmic Estimates and Data Interpretation
When reviewing public-avatar signals, teams must understand the nature of the returned data. AvatarLookup provides appearance attributes such as presented gender, age range, hair color, skin-tone features, or appearance ethnicity. These data points are algorithmic estimates derived from an avatar image and serve as auxiliary references for contact-data workflows. Organizations can use these algorithmic estimates to support internal review processes, but they must interpret the data correctly. Beyond the core avatar conclusion, the platform can also return source-specific public fields available for the queried account. By treating these attributes as supplementary context, teams can responsibly incorporate public profile signals into their contact-data workflows without overstating the certainty of the algorithmic outputs.
Operationalizing Contact-Data Review
To manage large volumes of contact data efficiently, teams can utilize asynchronous bulk processing capabilities. AvatarLookup supports bulk tasks for WhatsApp, Telegram, Viber, LINE, Zalo, MAX, Gmail, Yandex, and Mail.ru. Organizations can upload a bulk file containing up to 100,000 entries, provided the file does not exceed 10 MB and is formatted as a CSV, TXT, or XLSX document. During processing, the system evaluates the supported messaging and email identifiers, retaining clear avatar conclusions separately from invalid, failed, or undetermined rows. The core results distinguish between avatar available, no avatar, and undetermined. Teams must note that a "no avatar" result does not mean the account does not exist, and an "undetermined" outcome is not a negative result. By categorizing records into these distinct statuses, organizations can systematically review their contact directories, prioritize follow-up actions, and maintain high standards of data hygiene across their operational workflows.
Structuring Data Hygiene Workflows
Effective contact-data management requires structured workflows that integrate seamlessly with existing business operations. When teams implement public-avatar detection, they establish a standardized method for reviewing account identifiers before initiating outreach or updating internal databases. By utilizing source-specific public profile signals, organizations can append available public fields to their records, enriching the context available to operational teams. This structured approach allows departments to segment contact lists based on the presence of an avatar or specific public attributes. For example, records returning an "avatar available" status can be routed to one review queue, while "undetermined" records might undergo a different administrative process. By relying on the concrete outputs of AvatarLookup, businesses can build predictable, repeatable data hygiene routines. This systematic categorization supports better resource allocation, helping teams focus their efforts on well-documented contact records while maintaining a clear audit trail of the public signals retrieved during the review process.
Aligning External Signals with Internal Systems
Integrating external public-avatar signals with internal directories enhances the overall utility of a federated identity management implementation. While the federated system governs access and authentication, the external signals provide ongoing visibility into the status of the associated contact identifiers. Teams can periodically run bulk avatar checks against their user databases to confirm that the phone numbers and email addresses on file remain associated with public profiles on supported platforms. This alignment helps organizations identify discrepancies between internal records and external platform data. If a previously available avatar becomes undetermined, administrators can flag the record for manual review. By continuously monitoring these source-specific public fields, businesses maintain a dynamic understanding of their contact data. This proactive approach to data hygiene supports operational teams in working with the most current auxiliary references, informing more efficient communication strategies across the organization.
FAQ
How does FIM improve security for business applications?
Federated identity management implementation centralizes authentication through trusted identity providers. By supporting single sign-on across disparate applications, it reduces the number of passwords users must manage, thereby minimizing password fatigue and lowering the risk of credential-based attacks. This centralized control allows administrators to maintain consistent security policies, monitor access logs effectively, and streamline onboarding or offboarding procedures across the entire organizational infrastructure.
How should teams interpret algorithmic appearance estimates?
Appearance attributes like presented gender, age range, hair color, skin-tone features, or appearance ethnicity are algorithmic estimates derived from an avatar image. Teams should treat these data points strictly as auxiliary references to support internal contact-data review workflows. They provide supplementary context when categorizing and managing account identifiers, rather than serving as definitive demographic facts.
How do organizations process bulk contact-data reviews?
Organizations can use asynchronous bulk processing to review large volumes of identifiers. AvatarLookup allows teams to upload a CSV, TXT, or XLSX file containing up to 100,000 entries and up to 10 MB in size. The system processes these files to return core results—avatar available, no avatar, or undetermined—for platforms like Telegram, Viber, LINE, Zalo, MAX, WhatsApp, Gmail, Yandex, and Mail.ru.