Product guidance
What is Federated Identity Management? A Guide for Modern Businesses
Learn how Federated Identity Management (FIM) works, its security benefits, and how it differs from public profile data retrieval in business workflows.
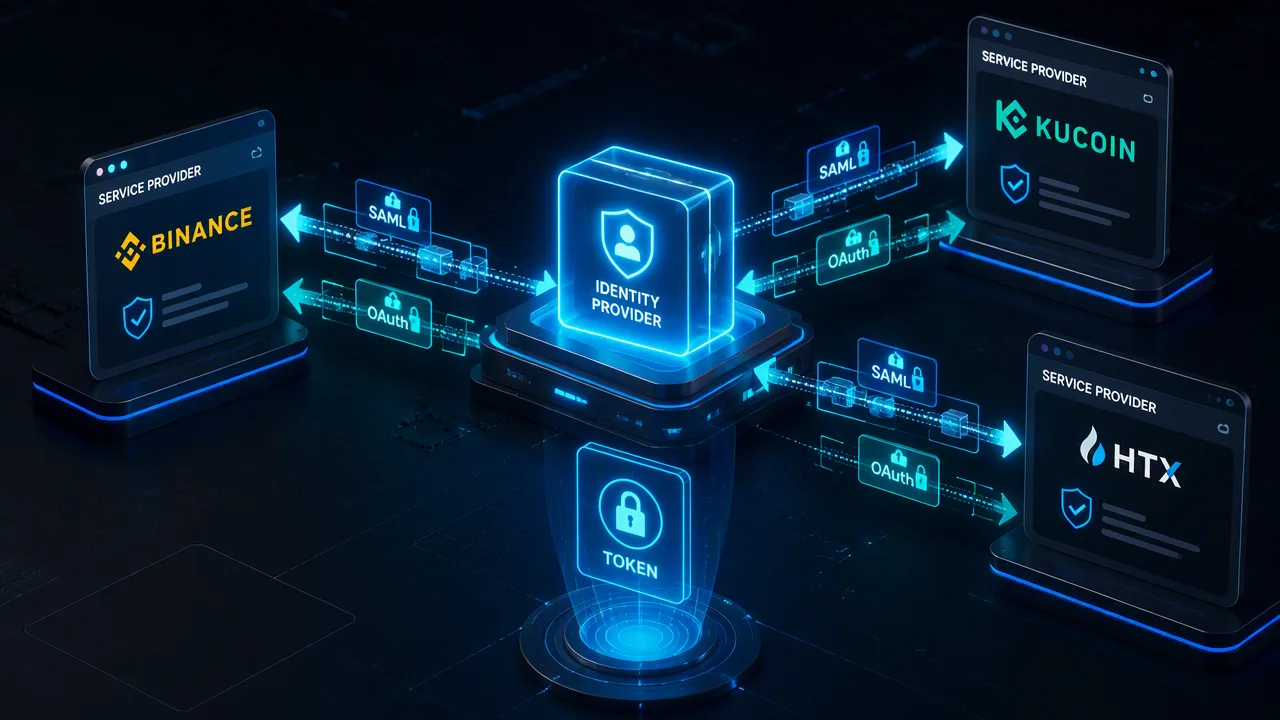
An overview of Federated Identity Management (FIM), explaining how trust agreements and standardized protocols support centralized authentication, and how FIM differs from public profile data retrieval.
Federated Identity Management (FIM) is a framework that helps users access multiple services using a single set of credentials. By establishing trust agreements between identity providers and service providers, FIM reduces login friction and supports centralized identity verification. This approach helps organizations minimize the risks associated with managing scattered, redundant user credentials across different platforms.
Understanding Federated Identity Management
Federated Identity Management (FIM) serves as a foundational strategy for modern digital ecosystems, helping users navigate multiple applications without the burden of managing separate accounts for each one. At its core, FIM relies on trust agreements established between two primary entities: the Identity Provider (IdP) and the Service Provider (SP). The Identity Provider is the centralized entity responsible for authenticating the user and storing their core identity information. The Service Provider is the external application, software, or service that relies on the IdP to verify the user's identity before granting access. For example, an employee might use a single set of corporate credentials to access an email client, a human resources portal, and a project management tool. Instead of each application verifying the user independently, they all defer to the central IdP. This framework helps organizations maintain control over their internal systems while providing a seamless user experience across a distributed network of services.
The Core Mechanism: How FIM Works
The operational foundation of Federated Identity Management is a secure communication process often referred to as a "handshake" between the identity provider and the service provider. When a user attempts to access a service, the SP does not ask for a password. Instead, it redirects the user's request to the trusted IdP. The IdP then prompts the user for their credentials—or verifies an existing active session—and authenticates the user. Once authenticated, the IdP generates a secure token containing the necessary identity assertions and sends it back to the SP. The SP validates this token and grants the user access to the application. This handshake is made possible by standard protocols that facilitate the secure exchange of identity information. Common protocols include Security Assertion Markup Language (SAML), which is widely used in enterprise environments; OAuth, which handles authorization and access delegation; and OpenID Connect, which adds an identity layer on top of the OAuth framework. These standardized protocols ensure that different systems can communicate securely, regardless of their underlying architecture.
Benefits for Business Security and User Experience
Implementing FIM offers significant operational advantages for both IT departments and end-users. From a user experience perspective, FIM reduces login friction by eliminating the need for multiple passwords across different platforms. Users spend less time recovering lost passwords and navigating login screens, which supports productivity and reduces frustration. From a security standpoint, centralized identity management improves security by reducing the attack surface of scattered user credentials. When users are forced to create multiple accounts across various service providers, they frequently reuse passwords. If one service provider suffers a data breach, those reused credentials can be exploited to access other systems. By consolidating authentication into a single, highly secure Identity Provider, organizations limit the number of places where sensitive credentials are stored. This centralization also makes it easier for IT teams to enforce strong authentication policies, such as multi-factor authentication (MFA), across all connected services simultaneously.
Distinguishing Authentication from Profile Data
While Federated Identity Management handles the rigorous process of authentication, organizations often use other tools to gather context about a user or contact. It is critical to distinguish between authenticating an identity and retrieving public profile signals. Authentication confirms identity and grants access. In contrast, public profile signals provide auxiliary context, such as checking for avatar availability associated with a phone number or email address. Platforms like AvatarLookup support contact-data workflows by checking public-avatar availability. Single checks support platforms like WhatsApp, Gmail, Yandex, and Mail.ru, while bulk tasks can process files containing up to 100,000 entries for sources including Telegram, Viber, LINE, Zalo, and MAX. The core results of these checks distinguish between an avatar being available, no avatar, and undetermined. However, these signals are strictly informational.
FAQ
How does FIM contribute to security for organizations?
Centralized identity management contributes to security by reducing the attack surface associated with scattered user credentials. Instead of multiple applications storing separate passwords, authentication is handled by a dedicated identity provider, which limits the number of vulnerable credential repositories.
What role do protocols like SAML and OAuth play in FIM?
Standard protocols such as SAML, OAuth, and OpenID Connect facilitate the secure exchange of identity information. They provide the standardized rules and formats required for the identity provider and service provider to communicate and execute the authentication handshake.